Store-bought hardware crypto wallets had secret chips installed that enabled stealing crypto recovery phrases
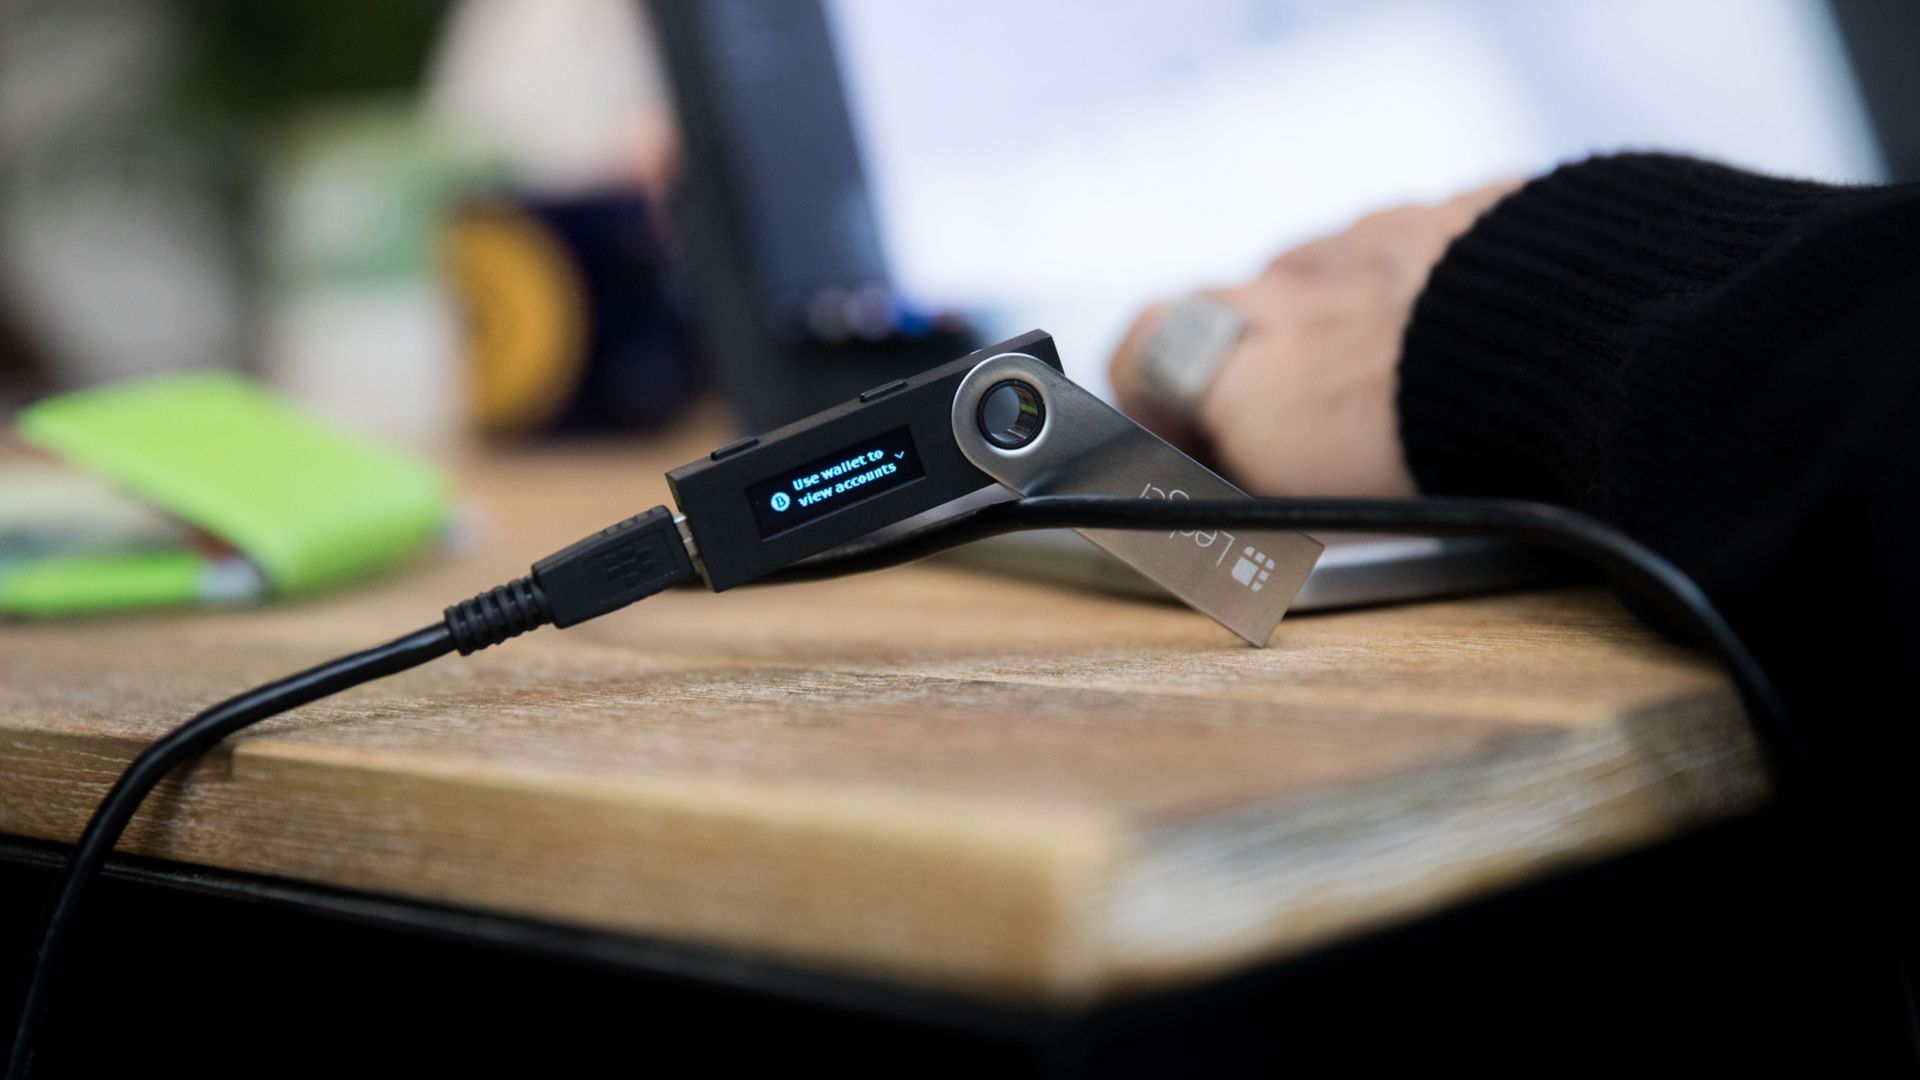
Cryptocurrency enthusiasts are often advised to acquire a hardware wallet like one of the Ledger models, theoretically adding the ultimate layer of security. And yet not even that approach is 100% safe, as a currently unfolding investigation revealed that Ledger resellers in Southeast Asia and Europe are carrying hacked wallets laden with eSIM and LTE modules for exfiltration of recovery phrases. At least $93 million (and going) has already reportedly been siphoned off users' balances. Hardware sold directly by Ledger is so far unaffected.
The first booby-trapped wallet originated from reseller Cryptobilis, which has currently ceased all sales of hardware wallets of all brands. The offending unit came from a store in Malaysia, though Cryptobilis also sells in Indonesia and the Philippines. Researcher Mark Karpelès has been looking into hacked wallets for a while now, and one of them came via Amazon Japan, bought from a Chinese seller and shipped from Malaysia. …
You're reading a preview. The full article is published by Tom's Hardware on their website.
Read the full story on Tom's Hardware