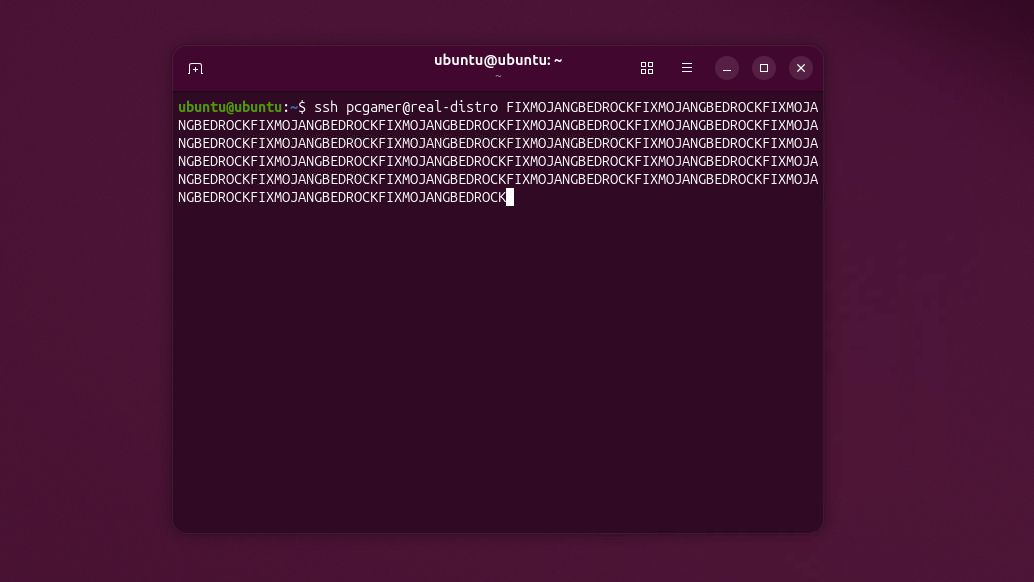
All that stands between a hacker and admin privileges on some Linux distros is a 257-character long string of literally anything
Some implementations of secure shell (SSH), one of Linux's most trusted and secure connection protocols, have been found vulnerable to the most peculiarly simple methods of bypass: spamming characters.
On some distros, simply type 257–1,024 characters and you get access to the root (admin) login. Thankfully, the list of vulnerable distros is quite small and niche, and OpenSSH has already issued a workaround/fix.
In some new release notes, OpenSSH explains that "this release contains a critical security workaround that affects Linux systems that use the musl libc and PAM disabled."
"Sshd(8): avoid password authentication bypass that is exploitable through sshd(8) that affects some Linux systems when built and run with PAM support disabled. We consider the root cause of this bug to be outside sshd, but it is exploitable via sshd and can be avoided there."
SSH itself is a longstanding and ubiquitous networking protocol that anyone who has dabbled even lightly in Linux networking projects will be familiar with. …
You're reading a preview. The full article is published by PC Gamer on their website.
Read the full story on PC Gamer