PHP2Shell: No login, no app code, no warning. What next?
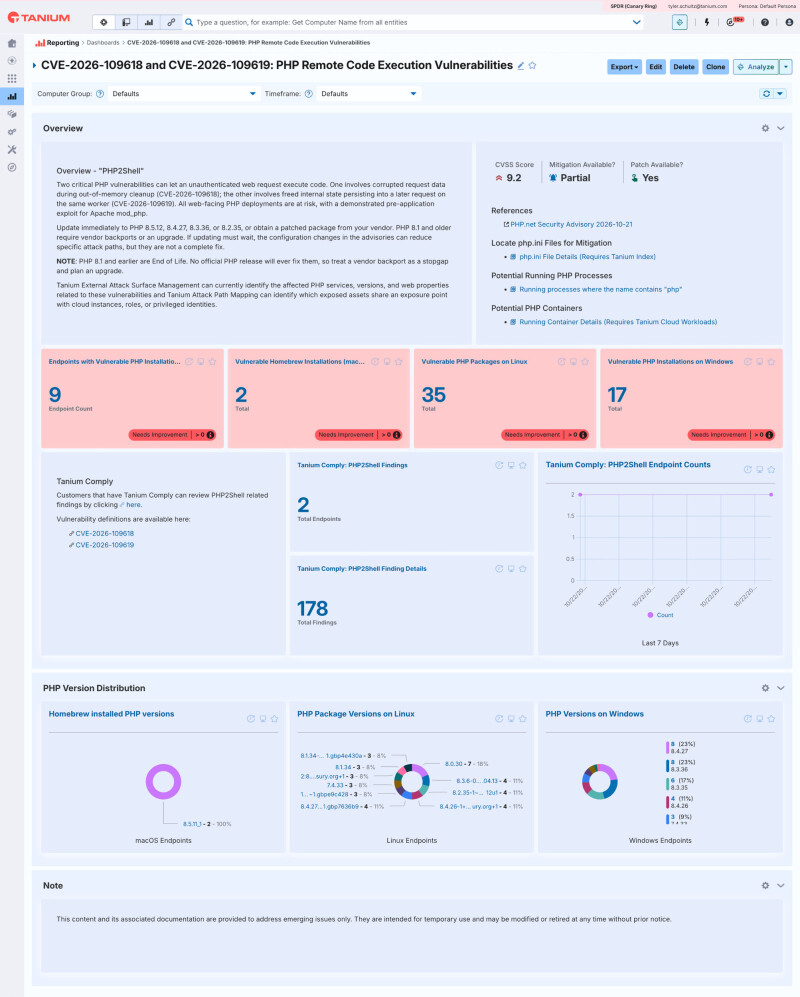
If you run PHP anywhere in your environment, patch to PHP 8.5.12, 8.4.27, 8.3.36 or 8.2.35 now. Two critical flaws disclosed last week, CVE-2026-109618 and CVE-2026-109619 (nicknamed "PHP2Shell"), let an unauthenticated attacker run code on a server with nothing more than a crafted web request. Both carry a CVSS v4.0 score of 9.2, every earlier release is affected, and exploitation in the wild has been reported.
The patch is the easy part. The hard part is finding every copy of PHP you own, because PHP rarely shows up where you expect it. This post covers what the flaws are, how far exploitation has gone, and how to get to full coverage fast.
Details leaked before the planned embargo, so the PHP security team moved fast and shipped fixes within about a day of announcing them.
Both bugs live in PHP core, not in any framework or plugin, so they reach anything that runs PHP to serve web requests.
Affected server …
You're reading a preview. The full article is published by The Register on their website.
Read the full story on The Register