Hackers leak info on 3,615 Trump Mobile subscribers, and that’s all they seemingly had
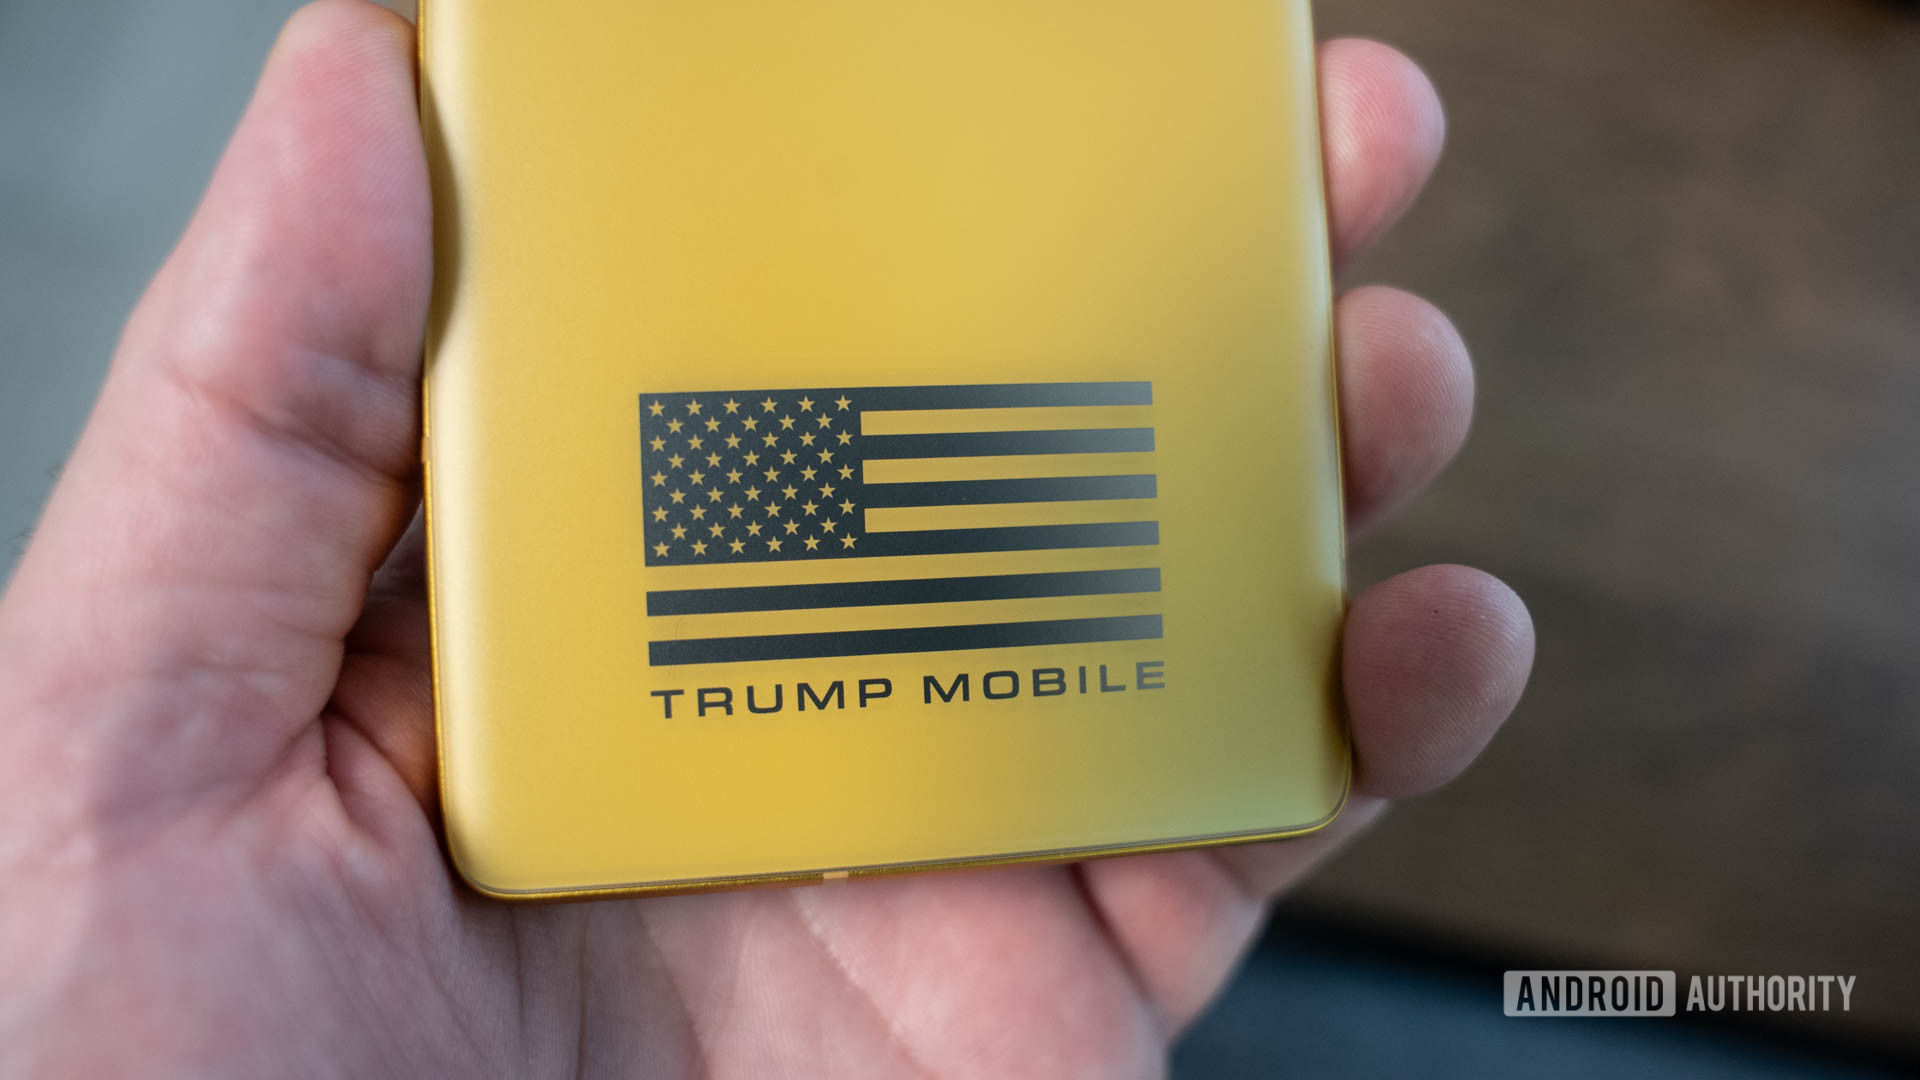
Credit: C. Scott Brown / Android Authority
TL;DR Threat actor group “BYOD” published 3,615 customer records belonging to Trump Mobile subscribers on the dark web.
Hackers allegedly gained entry via a remote access trojan (RAT) on an employee device at partner MVNO Liberty Mobile.
Exposed files include sensitive personal details of active subscribers and abandoned checkout data. However, this does not include data from Trump Mobile T1 phone orders.
Trump Mobile has already faced intense scrutiny this year over steep price hikes on its T1 smartphone, questionable hardware specs, and shipping delays. Now, the controversial smartphone brand is facing another major crisis after a hacking group published personal records allegedly belonging to thousands of its customers on the dark web. According to the threat actors, the compromised data exposes virtually the entire brand’s active subscriber base.
As reported by Straight Arrow News (via PCMag), a hacking group operating under the moniker “BYOD” claimed responsibility for exfiltrating and dumping customer files …
You're reading a preview. The full article is published by Android Authority on their website.
Read the full story on Android Authority